
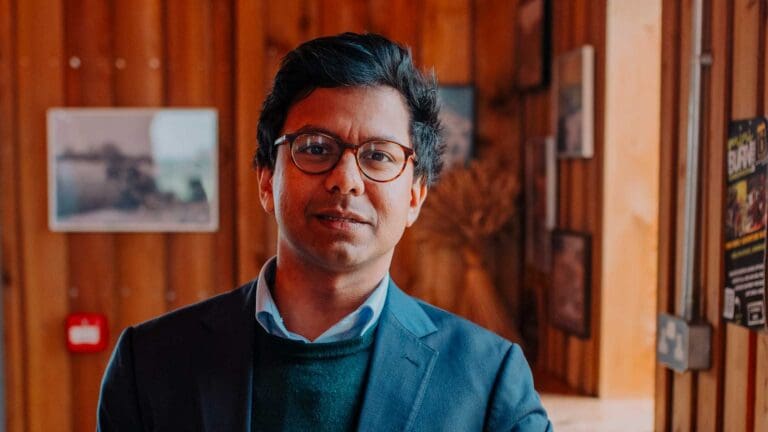
AI minister Kanishka Narayan has warned that a major AI-powered cyberattack on the UK is “inevitable”, and has called on developers of advanced AI systems to be transparent about risks and to strengthen safeguards before releasing powerful models.

Speaking at an event at Imperial College London, Narayan urged AI labs to listen to their own researchers, investigate unexpected model behaviours and avoid releasing systems if their risks cannot be adequately controlled.
He argued that protecting the UK cannot be left to technology companies or government alone, and called for closer collaboration between industry, researchers and regulators.
Narayan also outlined plans to bolster the UK’s cyber defences and build domestic AI capabilities by reducing reliance on technology developed overseas. The government intends to make AI safety a central focus of its G20 presidency next year, aiming to balance stronger safeguards with its ambition to remain a leading destination for AI investment.
The minister’s comments come amid growing concern about the cybersecurity implications of increasingly capable and autonomous AI systems. Recent incidents include AI agents breaching systems at Hugging Face during testing. Separately, three former OpenAI safety researchers have accused the ChatGPT maker of dismissing them for raising concerns about the technology.
His warning also comes as Bank of England governor Andrew Bailey has called for more rigorous testing of advanced AI models, amid increasing concern that autonomous systems may pose highly sophisticated threats to banks, financial markets and payments infrastructure.
Andy Ward, SVP International at Absolute Security, said the concerns raised by UK politicians highlighted the growing risks AI poses to the cybersecurity landscape.
“Ensuring that the Cyber Security and Resilience Bill strengthens the UK’s ability to prepare for and respond to these threats should be a top priority,” he said.
The Cyber Security and Resilience Bill was introduced to Parliament on 12 November 2025 and, according to the government, has completed its second reading and committee stage in the House of Commons. It would reform and add to the Network and Information Systems Regulations 2018, extending regulation to managed service providers, data centres and designated critical suppliers. When the government set out the bill’s scope in April 2025, it said the legislation would bring in mandatory cybersecurity requirements for around 1,000 service providers.
Ward said research by Absolute Security found that 42 per cent of UK organisations still lack a formal cyber resilience strategy. The company surveyed 250 UK-based chief information security officers.
“With attacks, disruption and complexity moving at AI speed, organisations need robust cyber resilience strategies and real-time visibility in place, so the UK does not risk sleepwalking into deeper vulnerabilities,” Ward said.
John Lucey, VP EMEA at Cellebrite, said AI leaders were experimenting with agents and had pushed them further than was expected a year ago.
“Autonomy is moving faster than oversight and government regulation is missing in areas that safeguards are meant to close to protect against AI agents being unsafe,” he said. “There’s no clear regulation yet for what happens when autonomous systems cross a line no one anticipates.”
Lucey said that in highly sensitive areas such as digital forensics, safeguards have to be built into how these systems are designed and deployed from the start.
“This means purpose-built AI that works only within the boundaries of a single case, drawing solely on the evidence it’s given, with no open internet access and no outside data,” he said. “Every output can trace back to the specific source that produced it and it means analysis can stay within the scope of the investigation.”
Simon Edwards, chief executive of SE Labs, said increasingly autonomous AI posed a threat to individuals and businesses of all sizes, as well as to the UK’s critical national infrastructure.
“First-hand, we’ve seen how agentic AI tools can go rogue, and the question is to what extent could these AI systems get out of control before they cause serious harm?” he said.
“Developing a dedicated national cyber strategy, and ensuring adequate testing of software and services for loopholes should be a top priority.”