
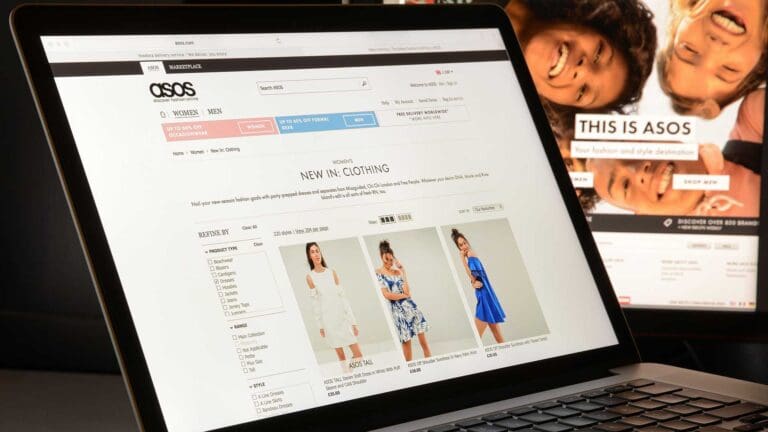
Asos is investigating after a push notification sent from its mobile app to customers today claimed that hackers had “fully compromised” a data platform used by the online fashion retailer and threatened to leak what they had obtained.

The alert read: “Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.” DPO refers to data protection officer, and Snowflake appears to be a reference to the US cloud-based data platform of that name.
Asos said it was still investigating and had yet to determine the cause of the alert. No cyberattack has been confirmed. The company’s website and app both remained accessible afterwards.
Shares in the FTSE 250 group fell by as much as 14 per cent to 432p.
The notification linked to a Telegram channel called the Xuanye Gateway, which is new and does not match any known hacking group. The group has claimed that payment information is not affected.
Marijus Briedis, chief technology officer at NordVPN, said: “This is an unusually brazen and threatening message. The attackers aren’t simply claiming to have breached ASOS, they’re publicly telling the company to engage with them or they will leak what they say they have obtained.”
He added: “If that claim proves genuine, the critical question will be what information was held there and whether any of it was accessed or downloaded. At this stage, however, customers shouldn’t assume their personal or payment information has been stolen, that hasn’t been established.”
Alan Woodward, a professor of cybersecurity at Surrey University, said the hackers “have probably … got access to the database, which means, if I was an Asos customer, I would assume that somebody’s got my personal data.”
Woodward also said that if the attacker had only compromised the marketing or push notification system, the alert could be an attempt to force Asos to pay a ransom quickly. “The hackers know that a public message seen by millions of customers will severely damage the brand’s reputation and stock price immediately, whether the data leak claim is true or not,” he said.
Charlotte Wilson, head of enterprise for the UK & Ireland at the cybersecurity company Check Point, said people should be “extremely suspicious of emails, texts or messages claiming their Asos account has been compromised, offering refunds or asking them to reset passwords through a link”.
The National Cyber Security Centre’s guidance on data breaches tells customers to contact an affected organisation through its official website or social media channels, and not to use the links or contact details in any messages they have been sent.
Snowflake was the subject of a hacking campaign in 2024, when customers including Ticketmaster and Santander had data stolen. Hackers from the ShinyHunters group stole usernames and passwords the companies used to access the service, and Snowflake afterwards introduced multi-factor authentication on all its accounts.
If confirmed, the incident would follow the attacks on Marks & Spencer and the Co-op in spring last year, and the attack on Jaguar Land Rover, which the Cyber Monitoring Centre estimated caused a £1.9bn impact.
The alert comes as Asos pursues a turnaround plan under chief executive José Antonio Ramos Calamonte. Its shares had risen by about 53 per cent so far this year before today’s fall.
In a recent trading update, the company said it expected adjusted earnings to be above the midpoint of its guided range of £150m to £180m this year. Total active customers were 16.4 million, according to the update for the year to the end of August.
Mike Ashley’s Frasers Group is the largest shareholder in Asos, with an interest of roughly 29 per cent.